 Thông Báo Việc Làm
Account Security at 9bet.ad: What a Risk Advisor Checks Before Logging In
On a quiet Tuesday night, a user in Hanoi watches a live football match and decides to check an online account. The screen flashes a new notification: “New login detected — Ho Chi Minh City, 23:47.” The user has not touched that account in two days. In the next thirty seconds, a sequence of decisions determines whether a minor alert becomes a serious incident: does the user ignore it, click a link in the message, or pause and verify the activity?
This scenario plays out across Vietnam every week. It is not really about whether a platform is “good” or “bad.” It is about the gap between what a service promises and what a user can actually control. For anyone reaching 9bet.ad through a search result, a friend’s suggestion, or a referral page, that gap deserves attention before the first deposit.
What Users Actually Search For When They Look Up 9bet.ad
Search behavior around 9bet.ad rarely begins with one clean question. Vietnamese users type combinations such as “9bet có uy tín không,” “9bet đăng nhập lỗi,” “9bet rút tiền,” and “trang chủ 9bet.” In English, the queries become “9bet.ad login safe,” “9bet.ad review,” and “9bet.ad customer service.” The wording differs, but the underlying intent stays the same: Can I use this account repeatedly without exposing my identity, my device, or my money?
Many reviews assume that the only real concern is whether withdrawals work. That is an important concern, but it arrives late in the sequence of steps each user must complete. Before withdrawing, a user must register, verify personal details, sign in, keep a session active, and spend time on the platform. Every step creates a security decision. A person searching for a review is really searching for a pre-flight checklist.
Several secondary goals appear in the same search session. Users want to know whether the platform locks an account after too many failed password attempts, whether sessions expire after inactivity, whether two-factor authentication (2FA) is available, and how support agents react when someone reports a compromised account. These details seldom appear in bonus-focused reviews. They are the core of this article.
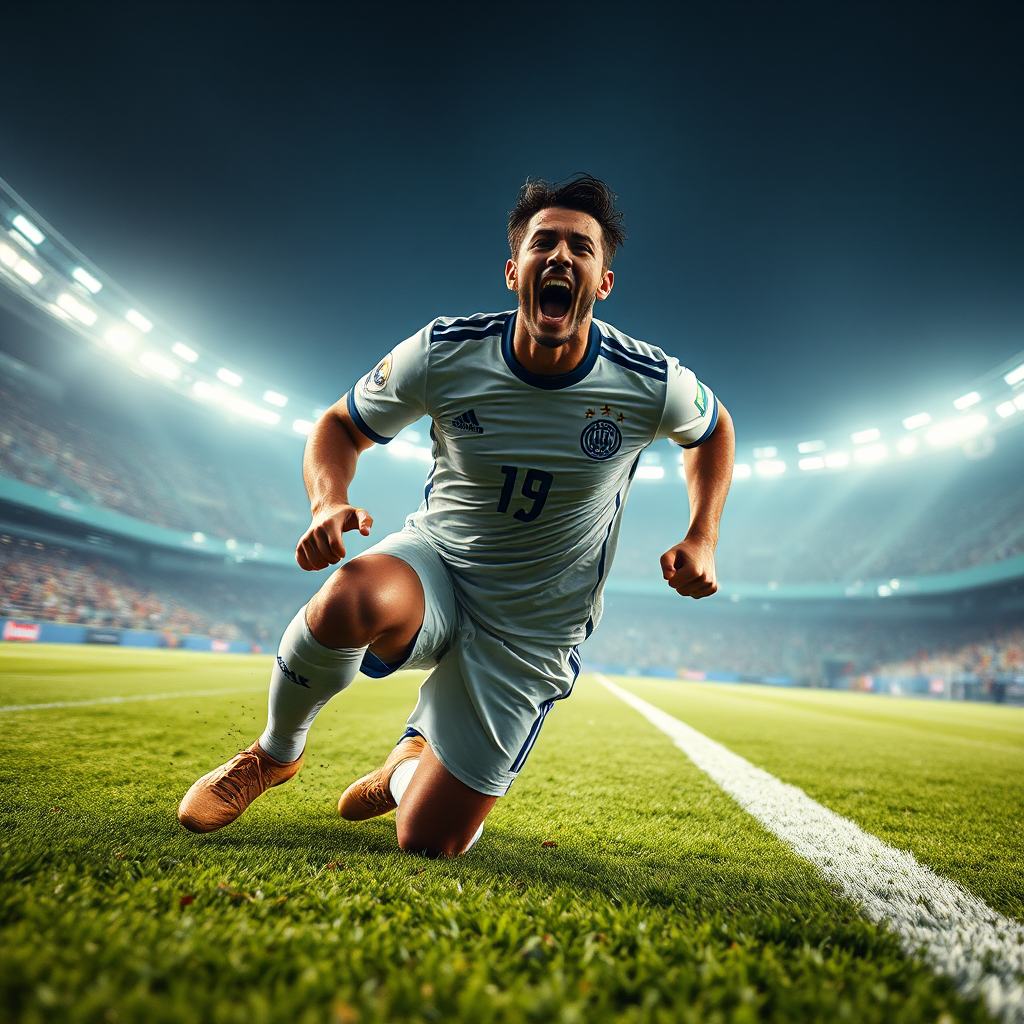
 Hình minh hoạ: 9BET
What a Risk Advisor Looks at Before the First Login
I cannot confirm a license number, a payout percentage, an official address, or a specific founding team for 9bet.ad. You should be cautious about anyone who claims those facts without providing public records. What I can offer is a verification framework that works for almost any online service, and it becomes especially important when a platform handles both personal identity and, possibly, real money.
Start with the domain itself. Check whether 9bet.ad resolves over HTTPS and whether the browser certificate matches the address. Look at the WHOIS record to see when the domain was created and whether the registrant details are public. A young domain paired with hidden registration information is not proof of fraud, but it raises the standard of inspection. An older domain with visible contact details makes the routine verification easier.
The content layer follows. Search the site for a privacy notice, a cookie policy, clear terms of use, and a visible responsible gaming statement. Even if those texts are short, their presence shows that the platform has considered legal transparency. Their absence is an early warning. For any betting-related operation, these documents are not decorative; they are the first evidence a user can rely on.
Many Vietnamese users arrive at 9bet.ad through referral pages rather than by typing the address directly. A local page such as quangcaopr.vn may host links, banners, or comparisons leading to the platform. That is a normal distribution channel in the region. Still, a referral link is not a guarantee. Before entering any credentials, verify that the URL in the address bar exactly matches 9bet.ad, and treat the referring page as a claim rather than a warranty.
A balanced assessment of 9BET therefore needs two perspectives at once: what the platform publishes in its official documents and what the user can personally verify at each login session. Neither perspective replaces the other.
A Step-by-Step Walkthrough of the Responsible Sign-In Routine
Most credentials are not stolen through sophisticated infiltration. They are exposed through careless habits: reusing one password across several services, clicking a shortened link that hides the destination, ignoring a browser warning, or staying signed in on a borrowed phone. A responsible sign-in routine takes only five minutes, but it must be repeated every time.
- Inspect the address bar before typing anything. Confirm the scheme is
https://and the domain is exactly 9bet.ad. Watch for lookalikes: a zero instead of the letter “o,” an extra hyphen, or a country-code suffix that differs from the expected one. If you came from a search engine, compare the link text with the visible URL. - Use a password generated by a password manager. Reusing credentials from an old forum or another gaming site is the quickest way to expose this account. No login page can protect you from a password that has already leaked elsewhere.
- Enable two-factor authentication if the platform offers it. Look for an authenticator app option, SMS verification, or one-time email codes. An authenticator app generally resists SIM-swapping better than SMS, but any second factor is better than none.
- Log in and immediately locate the session panel. Search for sections labeled “active sessions,” “devices,” “recent logins,” or “security history.” A well-designed platform shows a list of devices, locations, and recent times. If that information does not exist, treat the absence as a signal.
- Revoke every session you do not recognize. Many platforms allow you to invalidate all active tokens. If you use a phone at home, a laptop at work, and an old tablet in a drawer, remove the device you are not currently using.
- Review the session length policy. Some services keep a user signed in for two weeks; others expire after 30 minutes of inactivity. Decide which behavior matches your risk tolerance. A “remember me” checkbox can be convenient at home but creates exposure on any shared machine.
- Choose logout moments deliberately. At minimum, log out after using a borrowed device and immediately after you notice an unexpected login alert. One logout is often not enough; look for a “log out everywhere” option.
Notice what this routine avoids: clicking password-reset links sent to an unfamiliar phone number, letting the browser auto-fill passwords without checking the domain, and answering security questions with publicly discoverable data such as your birthplace or your mother’s maiden name. The password reset channel is the most popular attack path, because it converts a stolen email account into a stolen gaming account.
Another habit deserves a place in the routine: network awareness. Checking a balance over free hotel Wi-Fi or a café’s shared connection may place your session near people passively monitoring traffic. Clear HTTPS helps, but it does not make a hostile network safe. If you must log in from a public location, use a reputable VPN, or postpone sensitive actions until you are on a private network.
Risks That Actually Matter and How to Verify Them Independently
For a platform like 9bet.ad, the most realistic threats are not zero-day exploits. They are credential stuffing, phishing, and weak session management. A user who chooses a strong password is still exposed if the service stores session tokens carelessly or if a support agent can reset account details with insufficient proof.
Financial risk becomes tangible only when real money moves. Deposits, withdrawals, and occasional transaction errors turn the platform into a financial actor, not just an entertainment service. Once money is involved, the list of criteria expands: withdrawal limits, identity verification documents, processing windows, and the behavior of support when a withdrawal fails. None of these facts should be accepted from a single screenshot or an affiliate post. Verify them independently, ideally in writing.
| Verification signal | Red flag | Action to take |
|---|---|---|
| A clear privacy notice explains what data is collected, why it is collected, and how long it is kept. | No privacy notice, or a vague notice that names no data controller. | Do not enter personal data until the policy appears; request the controller’s identity. |
| A dedicated security panel displays device history, open sessions, and logout options. | No session history exists; the settings page contains only a password field. | Contact support and ask for a session audit; if none is possible, assume risk. |
| Two-factor authentication is available and cannot be removed through a simple SMS change. | No 2FA option, or support agents can disable security features without verification. | Act as if a stolen password wins automatically; keep the account balance minimal. |
| Withdrawal instructions are documented before a deposit, with KYC conditions clearly stated. | Support explains withdrawals only after a winning bet; limits and fees are hidden. | Confirm the policy by email; test with a small amount before committing more. |
Responsible participation means setting boundaries before you feel the pressure of a losing streak. If the platform provides deposit limits or loss limits, use them. If it does not, create your own rules: a fixed monthly amount you can accept losing, a cooling-off period after unusual bets, and an absolute stop when you feel the urge to reopen a session. These habits protect the user more than any promotional page ever will.
Frequently Asked Questions from People Who Care About Account Safety
Does having an account automatically mean my personal data is at risk?
No. Account creation carries risk only in relation to the platform’s data practices. Read the privacy notice, look for the data controller, and ask support what happens to your identity documents after verification. If the answers do not satisfy you, keep the relationship read-only.
What should I do first if I receive a login notification I did not trigger?
Do not click any link inside the notification. Open a fresh browser tab, type 9bet.ad manually, and inspect the account area. Change the password, review active sessions, and revoke all devices. Contact support only through the official channel shown on the site, never through the phone number written in the alert message.
Is a strong password enough to protect a live session?
Only partially. A strong password protects the login moment, but it does nothing after authentication. The session token, the 2FA configuration, and the device policy determine what happens next. Look for “active sessions” and “log out everywhere” controls to close the remaining exposure.
Should I use 9bet.ad on a public computer?
If any alternative exists, avoid it. Public computers may carry keyloggers, malicious browser extensions, or other users who recover an accidentally saved session. If there is no alternative, use a private browsing window, type the password manually, and completely close the browser when you finish.
How do I know whether a referral page such as quangcaopr.vn is trustworthy?
A referral page can be either a transparent affiliate site or an opportunistic link farm. Inspect the page’s own privacy notice and identify who wrote it. Then right-click the outbound link, copy the address, and compare it with the real domain. The link target matters more than the descriptive text around it.
When You Can Proceed and When You Should Pause
A security-conscious user does not need to wait for a hostile event to reveal the strength of a platform. The answer usually appears during a calm five-minute inspection. Use this checklist as your final test before you decide to make 9bet.ad part of your regular routine.
- URL inspection: the address bar shows
https://9bet.adwith no extra characters. - Documentation: the privacy notice, terms, and responsible gaming text are present and readable.
- Referral filter: if you arrived from quangcaopr.vn or a similar page, the cited link matches the real domain.
- Unique credentials: the password you intend to use appears nowhere else in your history.
- 2FA confirmation: you have enabled the strongest available second factor, not only a backup email.
- Session control: you can open the device history and revoke unrecognized sessions.
- Support check: you have sent one non-sensitive question and received a useful answer from a human process, not a generic auto-reply.
- Money boundary: if you deposit, you have already set a voluntary monthly limit and recorded it in your own accounting.
- Exit plan: you know where to change your password, how to request account closure, and where to report suspicious activity.
If every line behaves as described, proceed with reasonable confidence. If a single line fails — no certificate, no privacy text, no session management — the platform has already provided your review. The answer was there all along.